
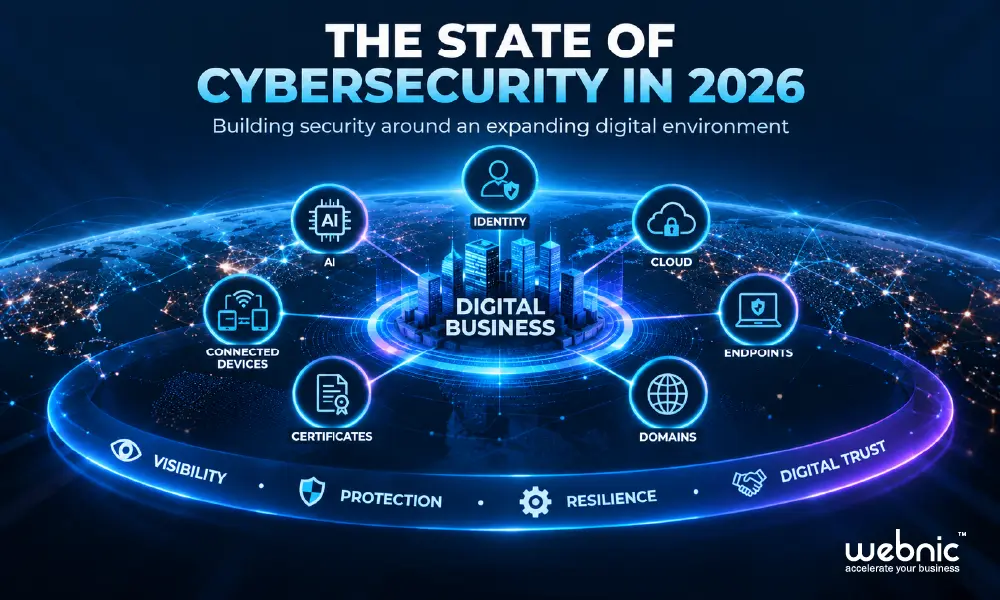
Cybersecurity is no longer simply about protecting computers, networks, and servers.
Businesses today operate across cloud platforms, websites, applications, employee devices, digital identities, domains, third-party services, and increasingly AI-enabled systems.
Every new connection creates an opportunity for the business.
It can also create another point that needs to be understood, managed, and protected.
As digital environments become more distributed, the cybersecurity question is changing from:
“How do we secure our network?”
to:
“How do we maintain visibility and control across everything our business depends on?”
That shift is shaping cybersecurity in 2026.
Identity security, exposure management, endpoint security, human risk, domains, connected devices, AI-powered security operations, and cloud security are increasingly connected rather than separate challenges.
Understanding those connections is becoming an important part of building stronger cyber resilience and Digital Trust.
Why Is Cybersecurity Changing?
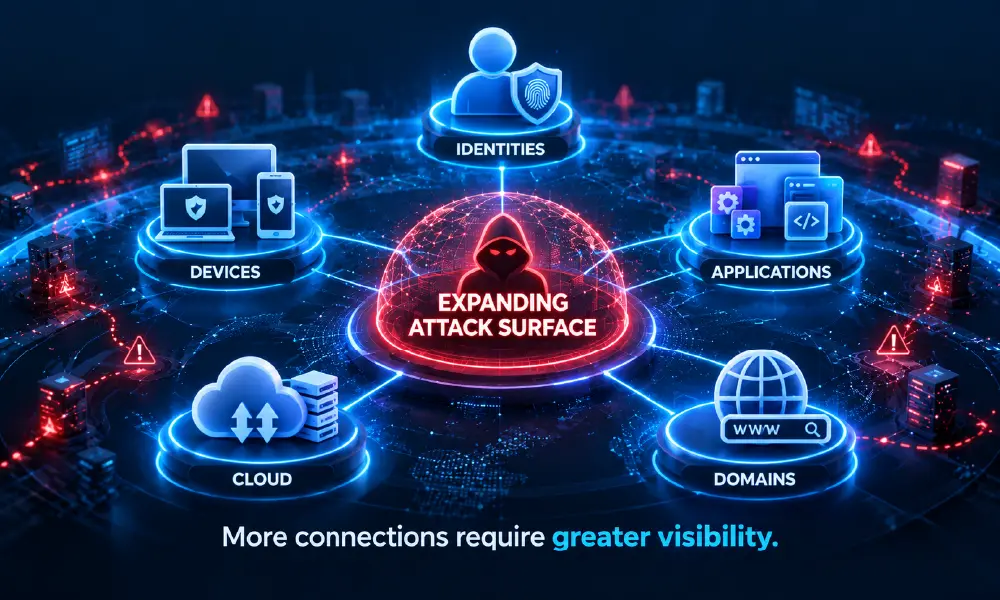
The traditional cybersecurity model was easier to visualise.
Employees worked from offices.
Applications operated within defined environments.
Security teams protected a relatively clear network perimeter.
That environment has changed.
A modern organisation may now operate across:
Employees & Customers
↓
Digital Identities
↓
Devices & Applications
↓
Cloud Infrastructure
↓
Domains & DNS
↓
Websites & Digital Services
↓
Third-Party Platforms
AI is adding another layer as businesses introduce AI applications, automated workflows, and non-human identities into their operations.
This means the modern attack surface is not one system.
It is the relationship between many systems.
Cybersecurity therefore increasingly depends on understanding those relationships and maintaining visibility across them.
1. Identity Is Becoming a Security Boundary
Identity has become one of the most important areas of modern cybersecurity.
Cloud services, remote work, software automation, and AI agents mean organisations are managing more identities than traditional employee accounts alone.
These may include:
- Employees
- Administrators
- Contractors
- Customers
- Applications
- Service accounts
- Automated systems
- AI agents
Each identity may have permission to access different systems and information.
The security question therefore becomes:
Who is requesting access?
↓
What should they be allowed to access?
↓
What privileges do they need?
↓
Does that access still make sense?
This is why identity security is moving towards stronger governance, continuous monitoring, and least-privilege access.
The objective is not simply to authenticate an identity once.
It is to continuously understand whether that identity should have the access it currently holds.
2. More Security Data Does Not Automatically Mean Better Visibility
Businesses generate enormous amounts of security information.
Endpoints generate events.
Cloud platforms generate logs.
Applications record activities.
Identity systems track authentication.
Networks, DNS infrastructure, and security platforms generate additional telemetry.
Collecting this information is important.
But collecting more does not automatically mean understanding more.
The challenge is increasingly:
Security Data
↓
Relevant Context
↓
Useful Visibility
↓
Faster Decisions
Security teams need to understand which information matters, how it should be structured and where it should be available when an incident occurs.
This becomes even more important as AI is introduced into security operations.
AI systems depend on the information available to them.
If security data is fragmented, incomplete or poorly structured, automated analysis may also lack the context needed to support effective decisions.
The goal should therefore not simply be:
“Collect more.”
A better question is:
“Can we turn the data we already have into useful security visibility?”
3. Endpoint Security Is Becoming Continuous
The endpoint environment has also changed.
Employees may work across:
Windows • macOS • Linux • Mobile Devices • Remote Environments
These devices may connect to corporate networks, cloud applications, and third-party platforms from different locations.
This makes the time between discovering a security weakness and addressing it increasingly important.
Endpoint security is therefore moving towards continuous:
- Patching
- Configuration management
- Vulnerability remediation
- Policy enforcement
- Monitoring
But not every vulnerability can immediately be patched.
Some systems may require operational testing.
Others may depend on software for which a fix is not yet available.
A practical approach becomes:
Patch What Is Patchable
↓
Mitigate What Is Not
↓
Continue Monitoring
The important change is that endpoint security becomes an ongoing process rather than a periodic maintenance exercise.
4. AI Is Changing Human Security
People have always been part of the cybersecurity equation.
AI is making that challenge more complicated.
Attackers can increasingly use AI to help create convincing:
- Phishing messages
- Voice impersonation
- Deepfakes
- Fraudulent conversations
- Social-engineering content
Traditional awareness programmes often teach employees to identify suspicious emails through obvious warning signs.
Poor grammar.
Unusual wording.
Suspicious formatting.
Those signals may become less reliable when AI can generate increasingly natural content.
The question changes from:
“Does this message look suspicious?”
to:
“Can I verify that this request is genuine?”
For organisations, human security therefore needs to extend beyond occasional awareness training.
Employees should understand how to verify unusual requests—particularly those involving credentials, financial transactions, sensitive information or changes to established procedures.
In an AI-enabled threat environment:
Recognition remains useful. Verification becomes critical.
5. Exposure Management Is Moving Beyond Vulnerability Counts
Finding vulnerabilities is important.
But finding them is only the beginning.
A large organisation may identify thousands of vulnerabilities across:
Applications
Servers
Cloud Infrastructure
Endpoints
Internet-Facing Systems
Treating every vulnerability as equally urgent is rarely practical.
Instead, organisations increasingly need to understand how individual exposures connect to actual business risk.
Consider two systems with the same vulnerability.
System A
Internal test environment
↓
Limited access
↓
No sensitive information
System B
Internet-facing application
↓
Connected to business systems
↓
Handles customer information
The vulnerability may be technically identical.
The potential business exposure is not.
This changes the conversation from:
“How many vulnerabilities do we have?”
to:
“Which exposures could create the greatest risk to the business?”
6. Domains, DNS and Email Are Part of the Digital Trust Chain
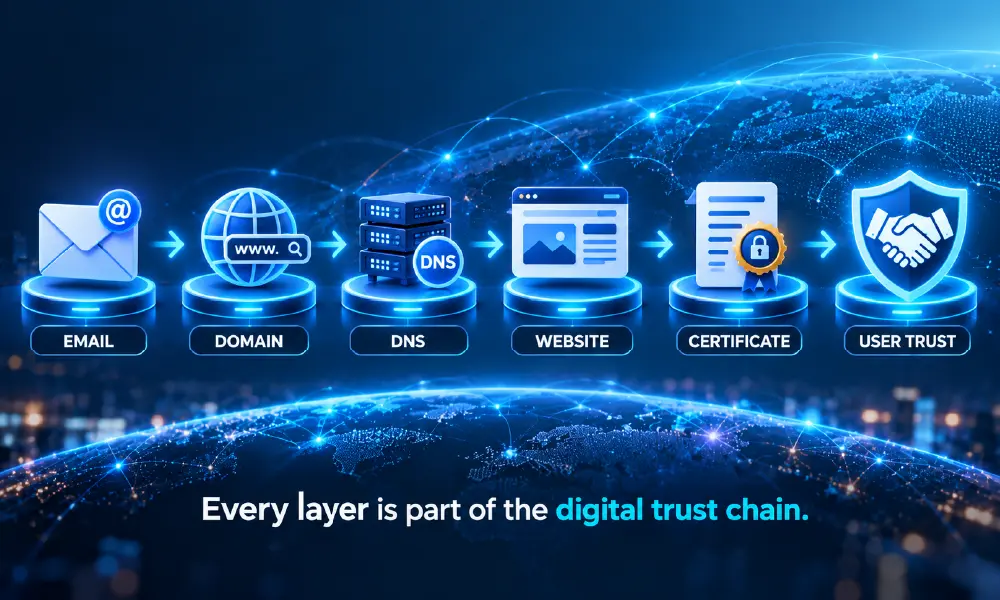
Cybersecurity does not stop at the organisation’s network.
Attackers can also operate outside it.
A fraudulent domain can imitate a trusted company.
A fake website can collect credentials.
DNS abuse can redirect users.
An impersonation email can direct customers towards malicious infrastructure.
Think about the journey:
↓
Domain
↓
DNS
↓
Website
↓
Digital Certificate
↓
User
Every step depends on trust.
This is why domain security is increasingly connected with broader cybersecurity and Digital Brand Protection.
A business may secure its internal systems while attackers create infrastructure outside those systems designed to imitate the organisation.
Maintaining visibility over domains and potential impersonation therefore becomes another part of protecting the digital presence of the business.
7. Digital Brand Protection Is Becoming Part of Cybersecurity
Brand abuse was traditionally viewed primarily as a trademark or reputation problem.
Today, it can also become a cybersecurity problem.
Consider a simple impersonation scenario:
Lookalike Domain
↓
Fake Website
↓
Brand Impersonation
↓
Customer Trust
↓
Credential or Information Theft
The attacker does not necessarily need to compromise the organisation’s own network.
Instead, they can exploit the trust customers already have in the brand.
Similar threats can appear through:
- Lookalike domains
- Fraudulent websites
- Fake social media accounts
- Executive impersonation
- Phishing infrastructure
- Unauthorised brand usage
This means businesses increasingly need visibility beyond their own infrastructure.
The question is no longer only:
“Is our environment secure?”
It is also:
“How is our identity being represented and potentially abused across the internet?”
8. Certificate Lifecycle Management Is Becoming More Important
Digital certificates help establish trusted and encrypted connections between users, systems, and digital services.
But certificates also need to be managed throughout their lifecycle.
The journey typically includes:
Discovery
↓
Issuance
↓
Deployment
↓
Monitoring
↓
Renewal / Replacement
As businesses operate more websites, applications, cloud services, and machine identities, the number of certificates they need to manage can increase.
Manual management can become increasingly difficult at scale.
A certificate that expires unexpectedly can create operational disruption even when no cyberattack has occurred.
This is where Certificate Lifecycle Management (CLM) becomes relevant.
CLM helps organisations approach certificates as continuously managed digital assets rather than individual files that someone needs to remember to renew.
For businesses, better certificate visibility and lifecycle management can help reduce manual processes and lower the risk of certificate-related disruption.
9. Connected Devices Are Expanding the Attack Surface
Not every connected business asset is a laptop or server.
Modern environments can include:
- Network appliances
- Sensors
- Cameras
- Internet of Things (IoT) devices
- Operational technology
- Specialised industry equipment
Each device can introduce another connection into the organisation’s digital environment.
Security teams therefore need to understand:
What Is Connected?
↓
What Is Exposed?
↓
What Vulnerabilities Exist?
↓
What Can Access It?
↓
What Happens If It Is Compromised?
This can be particularly challenging when devices support important operational processes and cannot simply be taken offline whenever a vulnerability appears.
Connected-device security therefore requires both visibility and practical risk management.
10. AI Is Changing Security Operations
Security teams face another challenge:
Speed.
Modern attacks can move quickly across identities, endpoints and cloud environments.
At the same time, security teams may need to investigate large numbers of alerts.
AI is increasingly being applied to help security operations teams:
- Analyse alerts
- Connect related events
- Summarise incidents
- Identify patterns
- Prioritise investigations
- Reduce repetitive manual work
A simplified security operation may increasingly look like:
Security Events
↓
AI-Assisted Analysis
↓
Context & Correlation
↓
Security Analyst
↓
Decision & Response
The important distinction is that AI can assist with speed and scale.
It does not remove the need for human judgement.
Security incidents often involve uncertainty, business context, and operational consequences that still require people to make informed decisions.
The opportunity therefore lies in combining:
Machine Speed + Human Judgement
11. Cloud Security Is Becoming Identity-Driven
Cloud infrastructure has changed how businesses deploy technology.
Applications, storage, databases, and workloads can be created rapidly.
But cloud environments also rely heavily on:
Identities
Permissions
Configurations
APIs
Credentials
An attacker with valid credentials may not need to exploit a traditional software vulnerability.
They may be able to use permissions already granted to the compromised identity.
This creates an important connection:
Identity
↓
Endpoint
↓
Cloud
↓
Data & Applications
Security teams therefore increasingly need visibility across these environments rather than treating them as completely separate security domains.
A suspicious authentication event may mean little on its own.
Combined with unusual endpoint activity, cloud privilege changes and unexpected data access, it may reveal something much more significant.
What Do These Cybersecurity Changes Have in Common?
At first glance, identity security, endpoints, domains, certificates, cloud environments and connected devices may appear to be separate cybersecurity problems.
They are increasingly connected.
Consider the modern digital business:
People
↓
Digital Identities
↓
Devices
↓
Applications
↓
Cloud Infrastructure
↓
Domains & DNS
↓
Certificates
↓
Digital Services
↓
Customers & Partners
A weakness at one layer can affect another.
A compromised identity can expose cloud infrastructure.
A vulnerable endpoint can provide access to business applications.
A fraudulent domain can target customers.
An unmanaged certificate can disrupt digital services.
A compromised connected device can introduce another route into the environment.
The common challenge is therefore:
Visibility + Control + Context + Response
What Should Businesses Prioritise in 2026?
Cybersecurity priorities will differ depending on the organisation, its industry and its digital environment.
But businesses can start with several fundamental questions.
- Do We Know What We Need to Protect?
Maintain visibility over important domains, identities, certificates, applications, cloud infrastructure, endpoints and connected assets.
- Do We Know What Is Exposed?
Understand which systems and digital assets are publicly accessible and where potential vulnerabilities exist.
- Do We Know Who Has Access?
Review human and non-human identities, privileges and authentication controls.
- Can We Detect Something Unusual?
Ensure security information provides enough context to identify abnormal activity.
- Can We Respond Quickly?
Define how incidents are investigated, contained and escalated.
- Can We Recover?
Understand how critical digital services would be restored following disruption.
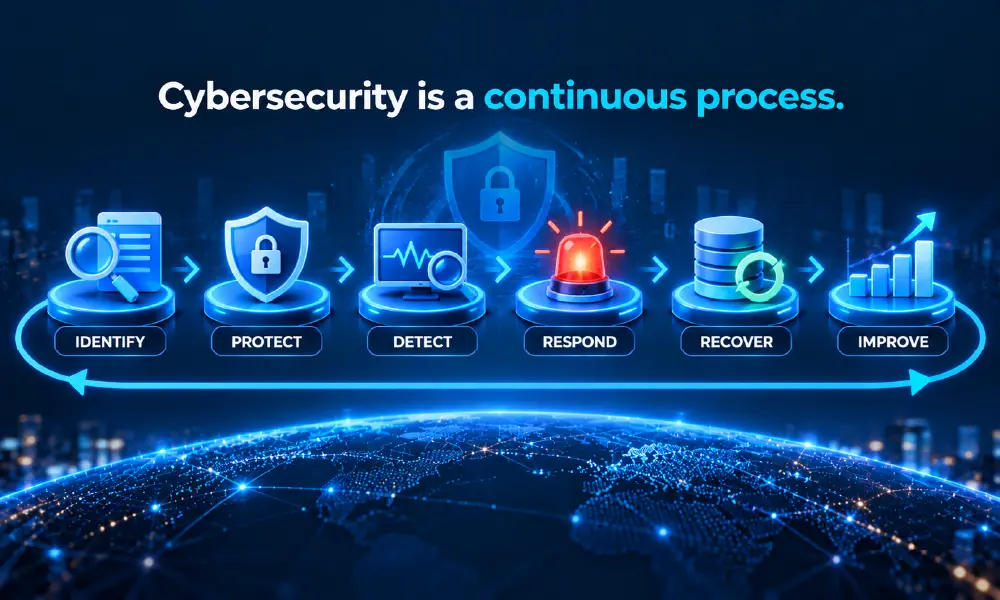
The cybersecurity journey increasingly becomes:
Identify
↓
Protect
↓
Detect
↓
Respond
↓
Recover
↓
Improve
Cybersecurity is not a one-time project.
It is a continuous process.
WebNIC Perspective
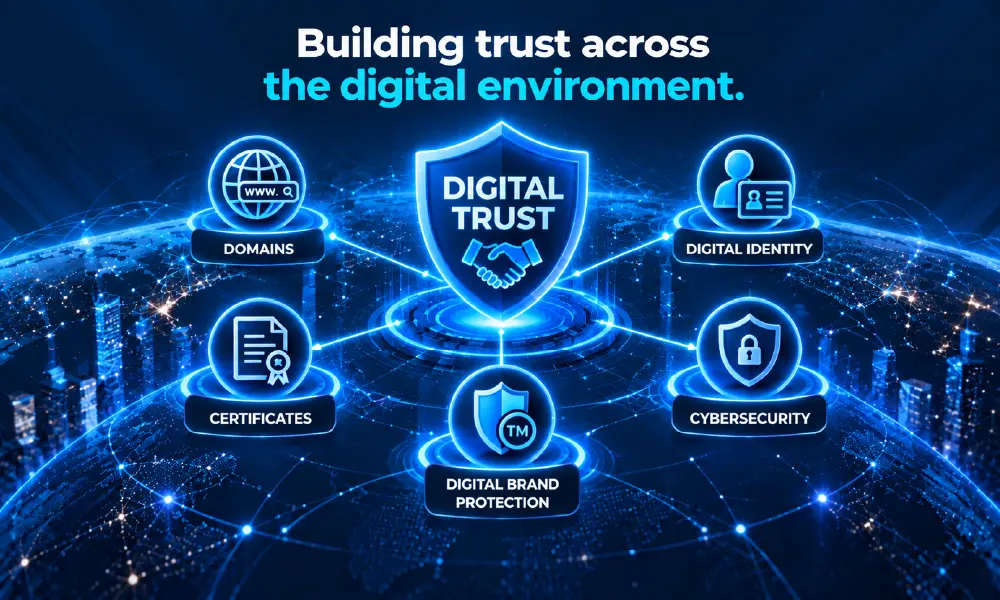
Cybersecurity is becoming increasingly connected to Digital Trust.
Businesses rely on customers trusting their websites.
Employees trust digital identities and authentication.
Applications depend on certificates.
Customers depend on domains to reach legitimate services.
Organisations depend on cloud platforms and connected infrastructure to keep operating.
This means the cybersecurity conversation is expanding beyond protecting individual systems.
The bigger question is:
“Can people and systems continue to trust the digital environment our business depends on?”
At WebNIC, we see several areas becoming increasingly connected:
Domain Management
↓
Digital Identity
↓
Certificate Lifecycle
↓
Digital Brand Protection
↓
Cybersecurity
↓
Digital Trust
Managing these areas effectively starts with visibility.
Businesses need to understand what digital assets they depend on, how those assets are managed, and where potential exposure can affect customers or operations.
As digital environments continue expanding, Digital Trust becomes less about one security technology and more about maintaining confidence across the entire digital ecosystem.
Frequently Asked Questions
Cybersecurity is increasingly moving towards continuous visibility, identity-focused security, exposure management, automation and resilience as organisations operate across more distributed cloud, device and digital environments.
Modern organisations depend heavily on cloud services, remote access, applications, service accounts and automated systems. As a result, controlling which human and non-human identities can access systems and information is becoming an important security boundary.
AI can affect both sides of cybersecurity. Attackers can use it to support more convincing social engineering and impersonation, while security teams can use AI to analyse events, correlate information and accelerate investigations.
Exposure management looks beyond simply discovering vulnerabilities. It considers which weaknesses are most relevant based on factors such as asset importance, accessibility, connectivity and potential business impact.
Domains form part of an organisation’s public digital identity. Attackers can use lookalike or fraudulent domains to impersonate businesses, create fake websites or support phishing campaigns.
Certificate Lifecycle Management (CLM) is the process of discovering, issuing, deploying, monitoring, renewing and replacing digital certificates throughout their lifecycle.
Attackers can misuse trusted brands through fraudulent domains, websites and impersonation. Digital Brand Protection helps organisations identify external threats that may target customers without directly compromising the organisation’s own infrastructure.
AI can help automate analysis and reduce repetitive work, but cybersecurity incidents still require context, judgement and decisions about business and operational impact.
Digital Trust is the confidence that digital identities, systems, assets and interactions can be relied upon to operate as intended. Cybersecurity is one of the foundations supporting that trust.
Start with visibility. Understand the identities, domains, certificates, applications, cloud infrastructure, endpoints and other digital assets the organisation depends on, then identify where the greatest exposure and business risk exist.